OT Cybersecurity Monitoring for Transmission Networks
Transmission networks cannot trade operational availability for cyber visibility. This engagement combined OT event monitoring, centralized security analytics, industrial network testing, vulnerability assessment and incident response preparation to give transmission stakeholders a stronger basis for understanding cyber activity, validating controls and protecting service continuity.
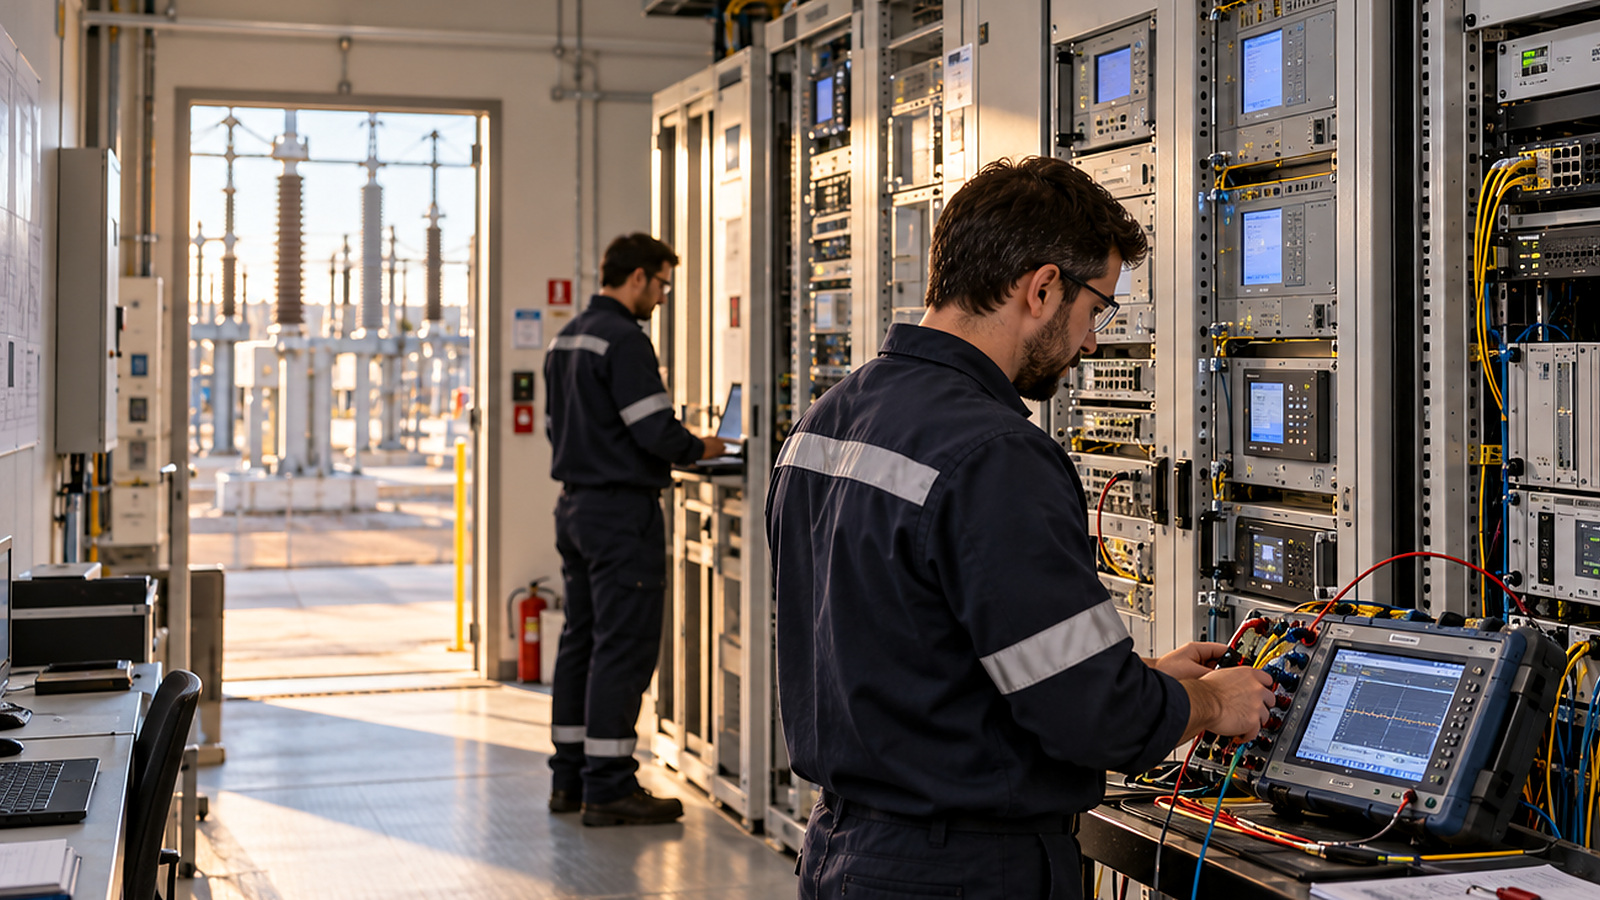
Transmission cybersecurity engineers test protection, communications and monitoring equipment inside a substation control room while the live switchyard remains visible through the doorway.
15 months
Documented programme duration
1 FTE
Documented core delivery team
Cyber event visibility
Improved visibility of cyber events across OT assets
Control assurance
Stronger evidence of technical security control effectiveness
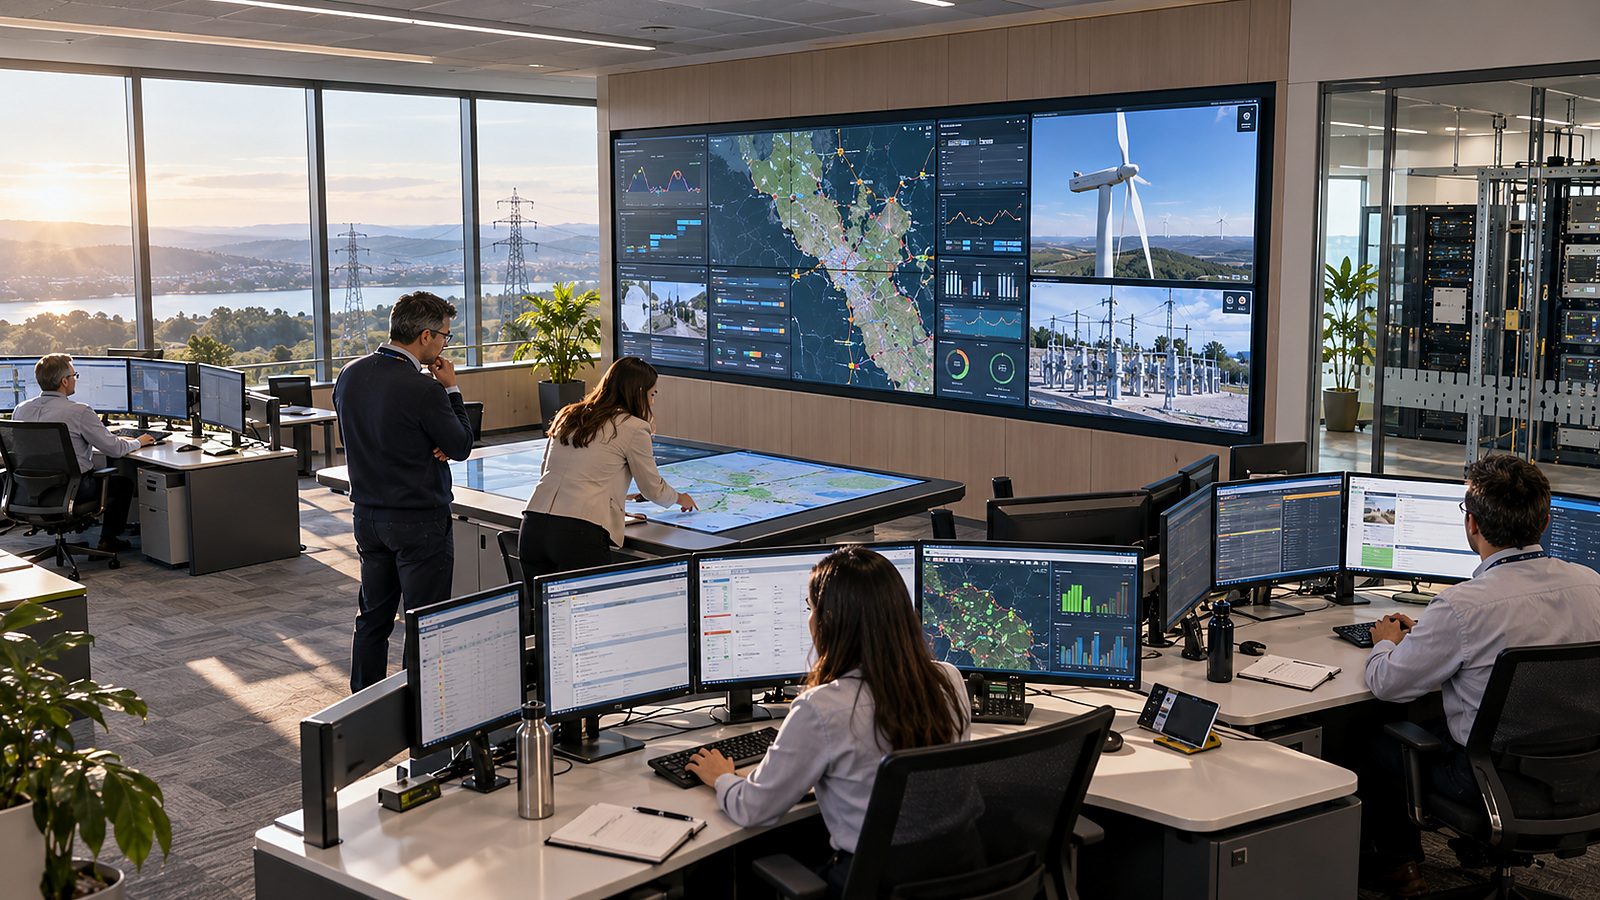
Utility operations team monitors transmission assets and security information across a large wall display and multiple workstations in a modern control centre.
Strengthening cyber visibility across transmission operations

An OT cybersecurity monitoring and assurance programme connected cyber event detection, centralized logging, industrial network testing, vulnerability analysis and response preparation around the availability requirements of transmission operations.

Detect events. Validate controls. Protect continuity.
目的
Establish an OT specific cybersecurity capability that could detect and interpret cyber events across transmission assets without disrupting highly available industrial operations. The programme needed to improve monitoring coverage, test whether technical safeguards operated as intended and help teams prepare for incidents in an environment shaped by diverse assets, legacy protocols and tightly coupled operational dependencies.
機会
As transmission estates become more connected, the volume of security signals grows alongside the complexity of protecting control centres, substations and industrial communications. A coordinated monitoring and assurance model creates an opportunity to turn fragmented events and technical findings into a clearer operational picture, prioritize mitigations around real OT exposure and embed continuity and incident response considerations into day to day cyber governance.
Securing an always on transmission environment

The challenge was to strengthen detection and technical assurance across a diverse OT estate while preserving the availability of the operations being protected. Legacy protocols, technical dependencies and uneven monitoring coverage made IT centric security practices insufficient on their own.
主な課題
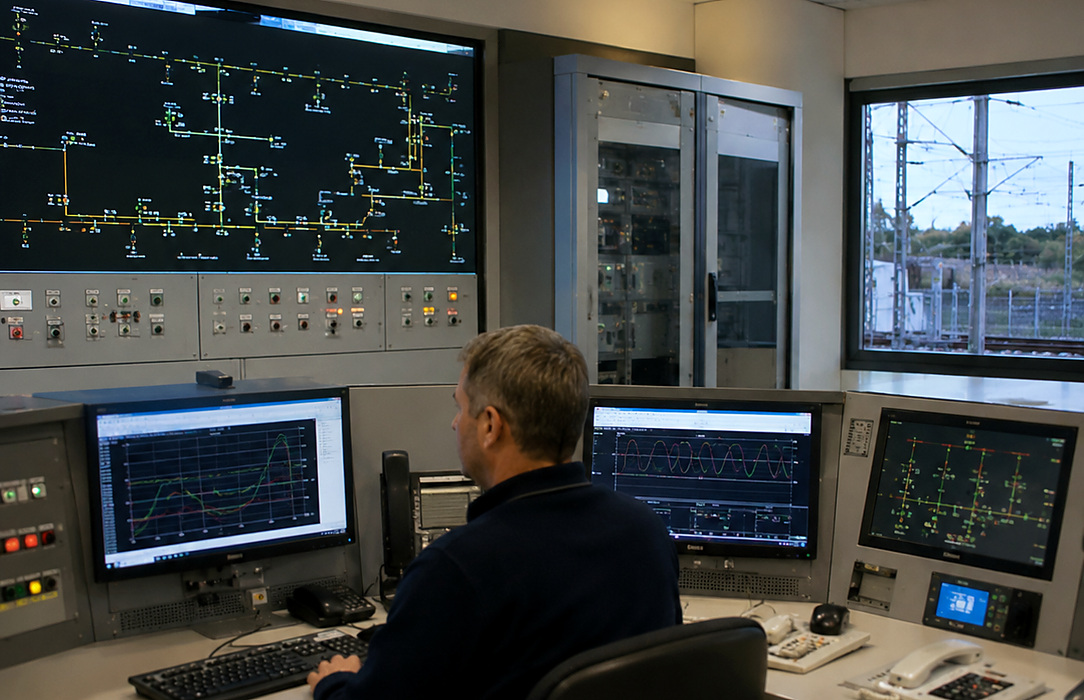
Operator monitors a transmission control room with legacy panels, one-line diagrams and multiple industrial displays supporting an always-on OT environment.
01 Detection without operational disruption
Transmission OT environments must identify cyber events while preserving high availability, leaving limited tolerance for intrusive or poorly adapted monitoring approaches.
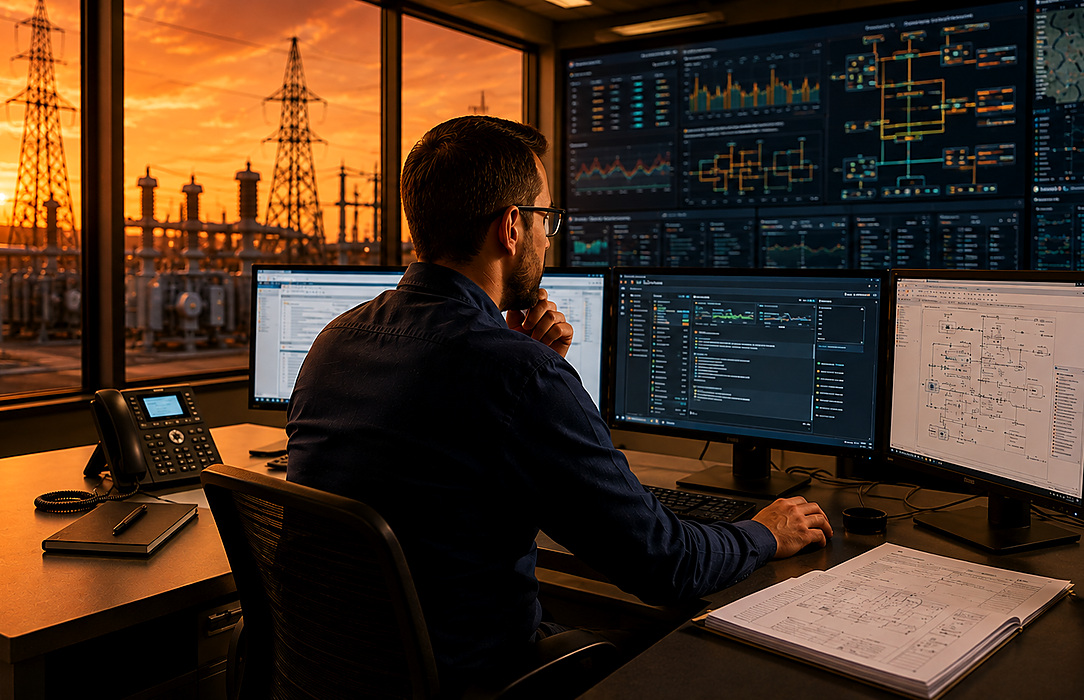
Transmission control-room specialist reviews multiple operational and network dashboards while the active electrical substation remains visible outside.
02 Uneven visibility across a diverse OT estate
Legacy protocols, heterogeneous assets and technical dependencies make it difficult to maintain consistent monitoring and asset classification across control centres and substations.
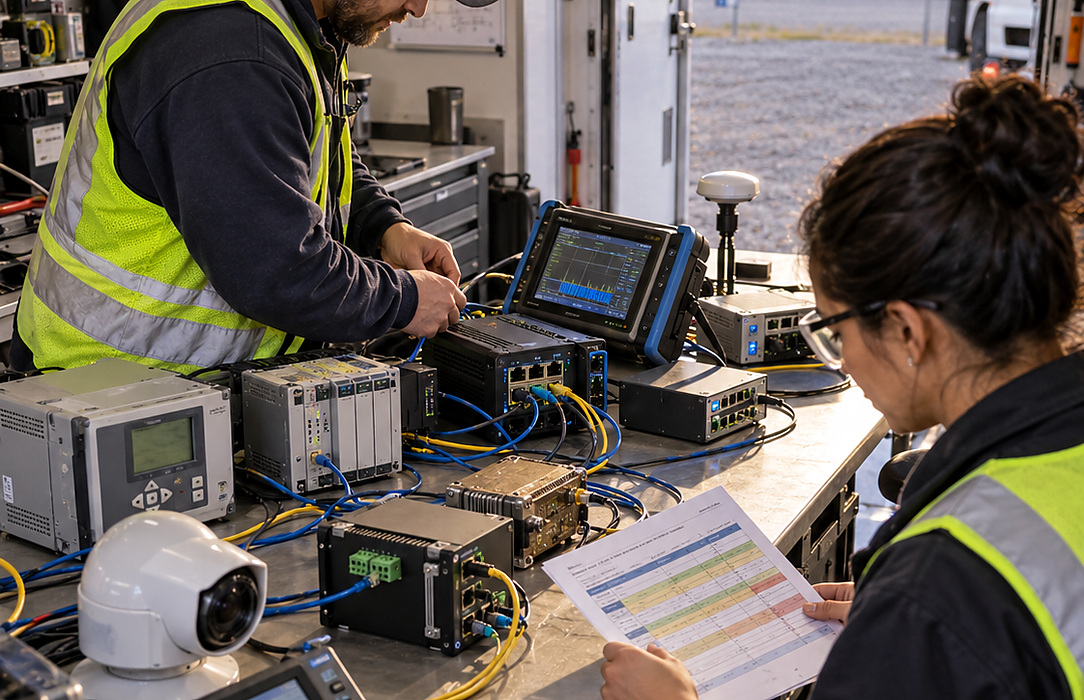
Field cybersecurity engineers test industrial network devices, protection equipment and communications links from a mobile substation engineering workspace.
03 IT centric assurance was not enough
Operators needed evidence that technical security measures were effective under real industrial conditions, not only conclusions based on conventional IT assumptions.
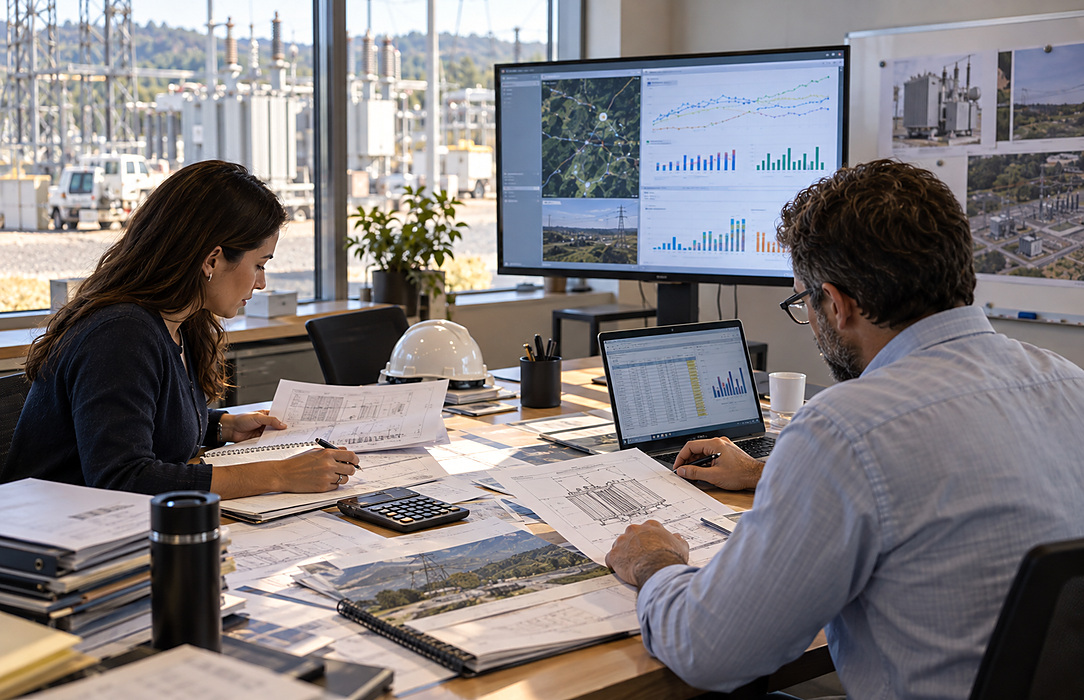
Utility cybersecurity and engineering professionals review transmission-site plans, asset information and mitigation priorities in a substation planning room.
04 Findings needed an operational response
Monitoring events, vulnerabilities and test results had to be translated into prioritized mitigations, continuity considerations and incident response actions that operational teams could use.
解決策
An OT specific monitoring and assurance model

NTT DATA combined ongoing monitoring support with centralized event integration, industrial network testing, vulnerability analysis and incident response preparation, linking detection, technical validation and mitigation within the operating realities of transmission networks.

チェックアイコン
Optimize OT cyber event detection

Supported cyber event detection and the optimization of OT monitoring systems around the availability and technical constraints of transmission operations.

チェックアイコン
Centralize security events

Integrated security system events into centralized logging and analytics using ELK and syslog patterns, giving teams a more coherent basis for reviewing activity.

チェックアイコン
Test industrial networks and prioritize exposure

Performed industrial network intrusion testing, vulnerability analysis and mitigation assessment to identify weaknesses and focus attention on the most relevant OT risks.

チェックアイコン
Validate controls and prepare for incidents

Assessed technical security measures, strengthened asset monitoring and classification, and defined continuity and incident response considerations for the transmission environment.

影響
Stronger visibility, evidence and OT cyber readiness

By linking monitoring, technical testing and response preparation, the engagement gave transmission stakeholders a stronger basis for identifying cyber events, validating safeguards and prioritizing mitigation. The capability improved visibility across OT assets, strengthened evidence of control effectiveness and improved preparedness for incidents that could affect service continuity.
ドラッグ