- All Foundries

- 商品管理と取引

- 顧客とマーケティング戦略

- デジタルエンジニアリング

- ステーション・スタジオ

- サプライチェーン&インダストリー5.0

- サステナビリティ

- Physical AI

- Next-Gen Infrastructure

Who Owns OT Cyber Resilience? Making Accountability Clear Across IT, OT and Operations
Industry 4.0 has connected enterprise systems, manufacturing operations and the shop floor more closely than ever. That creates value, but it also means a cyber event can cross organizational boundaries quickly. Conventional IT priorities do not transfer unchanged into OT, where safety, reliability, productivity, operational continuity, legacy systems and maintenance constraints shape every response. When ownership is unclear, teams can lose time deciding who prioritizes a vulnerability, approves a control, governs remote access, escalates an incident or leads recovery. The issue is not whether Cyber, IT, OT, engineering or operations should own resilience alone. It is whether they can make accountable decisions together before operations are under pressure.
OT cyber resilience depends on clear decision rights, operationally informed risk priorities and coordinated action across Cyber, IT, OT, engineering and operations.

Clarify who assesses OT cyber risk, approves controls, accepts residual risk and directs escalation across Cyber, IT, OT, engineering and operations.
Evaluate vulnerabilities and countermeasures against safety, reliability, productivity, continuity, legacy technology and maintenance constraints, not severity scores alone.
Agree how teams handle remote and third-party access, incident response, continuity and recovery before an event compresses the time available to decide.
Connect roles and responsibilities to asset visibility, context-aware risk assessment, strategic planning, mitigation, security operations and continuous improvement.
NTTデータのサポート体制は?
Reviews the attribution of cybersecurity roles and responsibilities through a RACI matrix, together with the policies, processes and procedures that support them.
Uses passive asset discovery, inventory and architecture assessment to show what is connected, how it communicates and where cyber risk meets operational consequence.
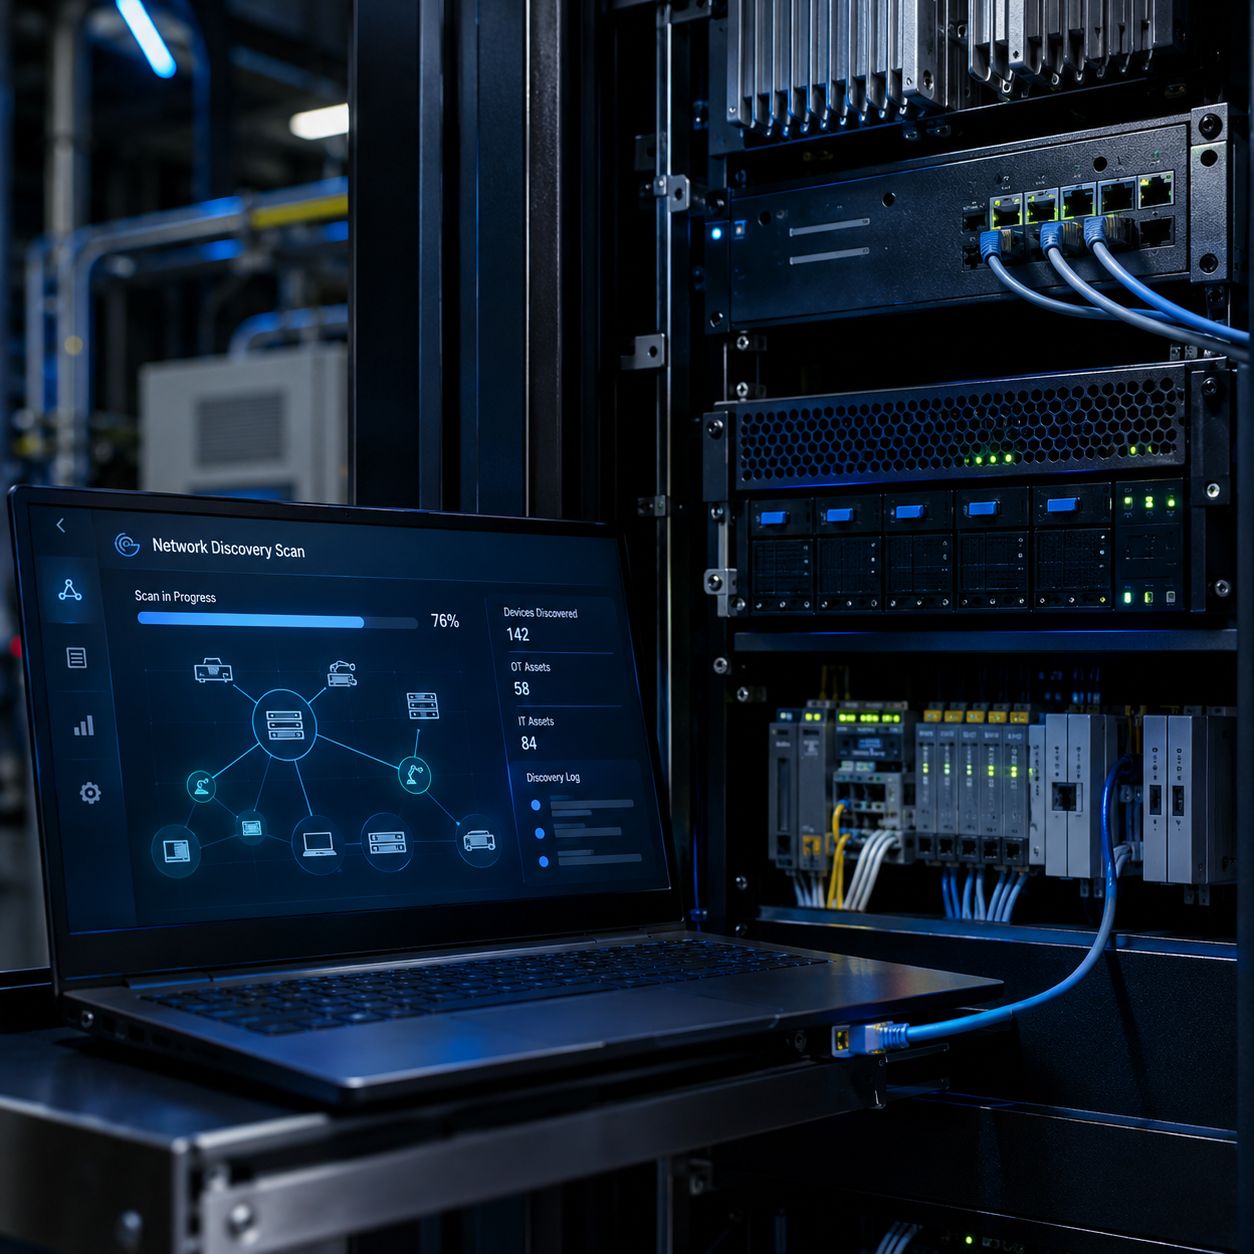
Translates assessment findings into a prioritized OT security roadmap, including segmentation, industrial DMZ design and stronger controls for remote access where appropriate.
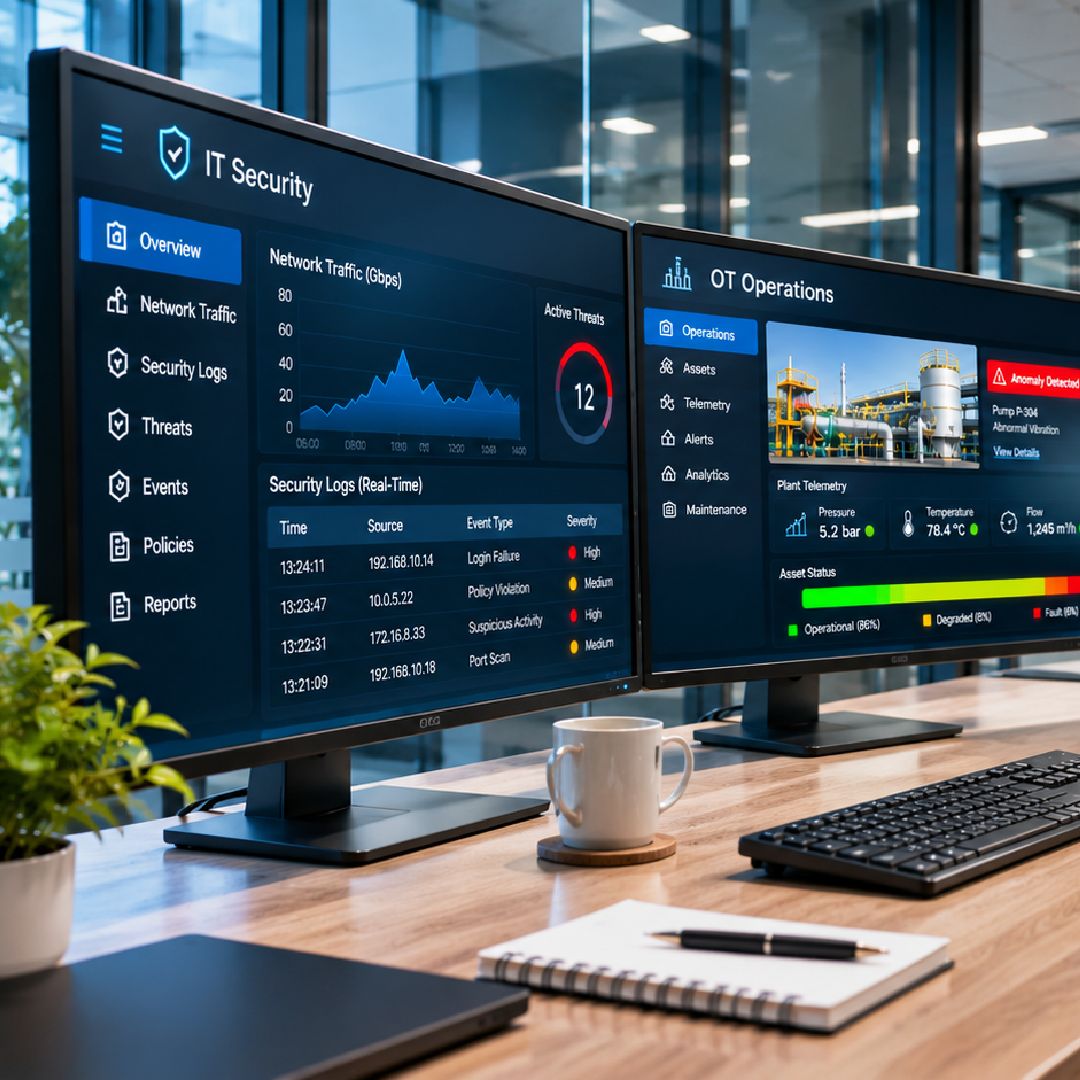
Connects continuous monitoring, anomaly detection and incident-response workflows with a Security Operations Center that brings OT security expertise into escalation and response.
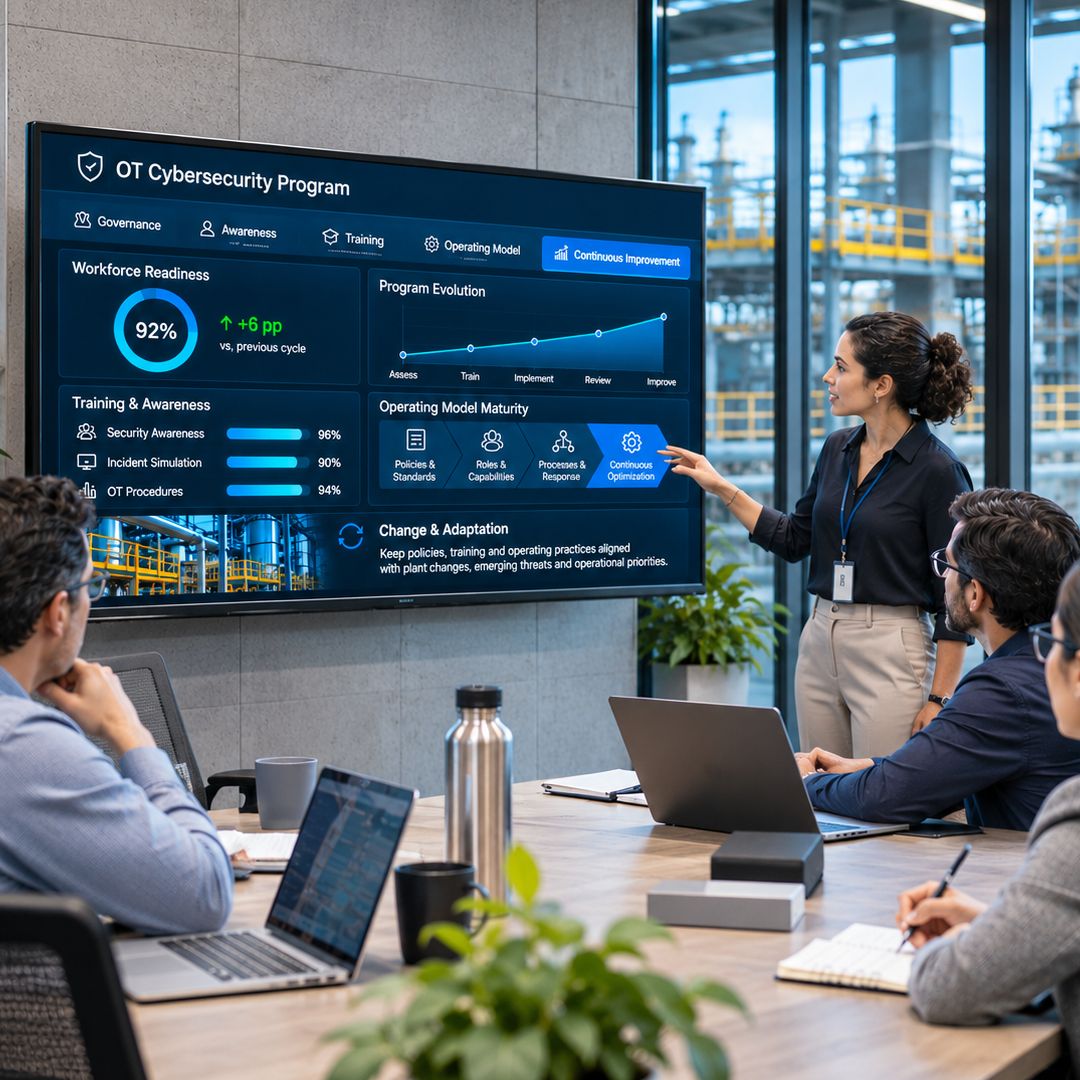
Helps organizations review policies, strengthen awareness and training, and evolve their operating model as plants, threats and operational priorities change.
Public client work shows how governance becomes stronger when it is connected to architecture, monitoring and day-to-day operations.
Industrial organizations are connecting IT and OT governance, layered security architecture and centralized monitoring to protect distributed operations while keeping access, risk and response aligned with plant priorities.
The teams worked with NTT DATA to design a multilayer OT security architecture aligned with IEC 62443 and adapted to the requirements of individual plants.
The manufacturer implemented multiple layers of secure architecture for plant-specific requirements, with industrial access limited according to operational needs and enterprise access controlled by its in-house IT team.
Its security teams consolidated OT and IoT asset visibility and risk monitoring through a centrally managed monitoring environment.
Real-time reporting, audits and OT monitoring were integrated with a central SOC, alongside training for security managers across the rollout.
Establish the decision rights, escalation paths and cross-functional coordination needed to strengthen OT cyber resilience.